
How to Remotely Access PLC and HMI Through an Industrial Cellular Router

Actualizado: hace 4 días
A remote engineer may need to inspect an HMI or upload a PLC program at a site that has only cellular coverage. A working SIM is the first link, not a complete access design. The route must reach the intended device, limit who can use it and distinguish observation from changes that affect the process.
An industrial cellular router can connect the machine LAN to a remote access service or VPN endpoint. Its exact VPN modes, ports, logging and recovery behavior depend on the selected model and firmware. Use this guide to specify the path and commission it; confirm device features in the current manual before purchase or deployment.
Choose an Access Boundary Before Opening a Port
Use an authenticated VPN or managed remote-access path with explicit user identity and a narrow allowlist as the starting design. CISA's remote-access guidance and NIST SP 800-82 Rev. 3 describe the need to control and monitor access to operational technology. A VPN carries traffic; it does not authorize an engineer to operate a machine or automatically limit the engineer to one PLC.
NAT solves an address-mapping problem. Inside a controlled VPN, it may help when several customer machines reuse the same private subnet; the same-IP PLC guide addresses that case. Public port forwarding is different: it makes a service reachable from outside the site and should not be treated as a substitute for user authentication, segmentation or an access gateway.
Avoid exposing a PLC or HMI service directly to the public internet. If a site must make a temporary exception, define its owner, permitted source, expiry, monitoring and removal before opening it.
Decision | Record before configuration |
|---|---|
Who connects | Named users or service identities; approval and revocation owner |
What they reach | Exact PLC/HMI addresses, services and required direction |
What they may do | Read-only monitoring, engineering changes or HMI control, with separate authorization |
How access ends | Session timeout, account removal, rule removal and retained logs |
Draw the Data and Address Paths
Sketch the remote engineer, the reachable VPN endpoint, the cellular WAN, the router LAN and each target PLC/HMI. The carrier may use private addressing or CGNAT, so inbound connections to the SIM may not be available; RFC 6888 describes inbound-application limitations of carrier-grade NAT.
A router-initiated outbound tunnel to an endpoint the team controls can work with those carrier arrangements, subject to the selected VPN design and firewall policy. Compare IPsec, OpenVPN and WireGuard against the actual endpoint and firmware support using the industrial VPN comparison.
For a simple example, the router LAN could be 192.168.10.1/24, a PLC 192.168.10.10, an HMI 192.168.10.20, and remote VPN clients in 10.8.0.0/24. These are illustrative addresses, not router defaults. Check the engineering laptop's local subnet and every customer site for overlap.
If two sites both use 192.168.1.0/24, plan site-specific translation or renumbering rather than assuming ordinary routing can distinguish them. If the PLC or HMI has no route back to the VPN clients, specify a return route or a documented translation design.
List the exact services the engineer needs. PLC discovery broadcasts may not cross a routed VPN; test the vendor tool with a manually entered device address where it supports one. A ping to the router proves neither PLC programming access nor HMI control.
Configure and Commission in Layers
Establish the WAN. Check SIM registration, APN, signal quality, data plan and the carrier's address type. Record the firmware and the intended recovery path.
Set the boundary. Deny unsolicited WAN access, disable unused management services and allow only the VPN endpoint and the necessary PLC/HMI destinations. Use individual accounts and the site's required authentication controls. Keep configuration backups and a rollback path.
Bring up the tunnel. Confirm endpoint identity, credentials or certificates, routes, DNS if needed and the allowed subnets. Test from an authorized remote client, not only from the router's own diagnostics.
Test the PLC. Check its IP, return path, firewall rule and vendor engineering service. Verify online monitoring before any program transfer. Treat an upload or download as a controlled maintenance action with backup, approval and a qualified person at the site when the process requires it.
Test the HMI separately. Verify the intended web, VNC or vendor service, user role and session timeout. A reachable PLC does not prove the HMI service is available or restricted correctly.
Record the source, target, port, user role and result for each test. If the tunnel connects but an application fails, compare routing and access rules before changing cellular settings. The sensor, PLC and Modbus path guide helps separate device data roles from IP transport.
Check Data Use and Recovery
A continuously refreshed HMI, remote desktop session or camera can consume data even when nobody is changing a PLC.
Measure representative active and idle sessions against the site's data plan instead of assuming a fixed allowance per hour. Check background polling, retries and sessions left open. Set alerts where the router or service supports them and retain enough logs to connect a usage spike to a session.
Test failure paths in an authorized window: cellular loss, VPN endpoint loss, router restart and credential revocation. Note whether the device reconnects and whether a remote session resumes with its prior privileges. Dual SIM or WAN failover is useful only if the selected hardware, service plans and configuration actually support the intended recovery behavior. Do not use a successful ping or a router health check as proof that PLC programming and HMI viewing still work after recovery.
What to Verify Before Choosing an Industrial Cellular Router
Start with the carrier bands and approvals for the country, power input, enclosure and temperature range, Ethernet and any required serial interface. Then verify the exact firmware's VPN mode, firewall rules, route or NAT controls, user management, logs and remote recovery.
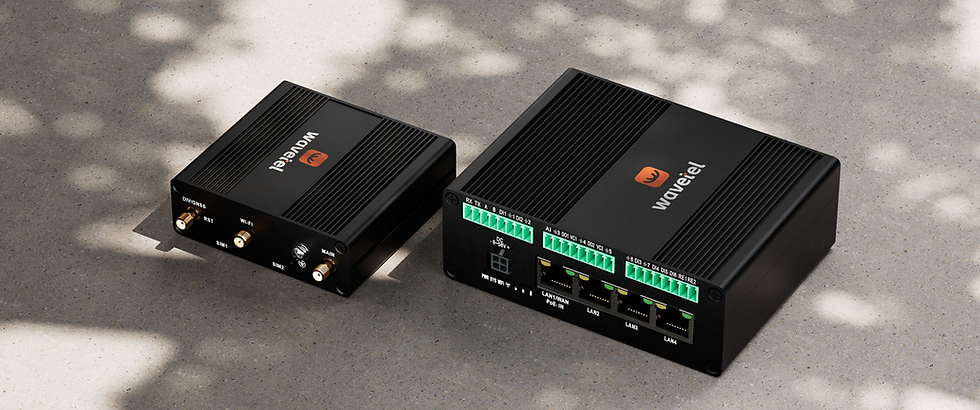
Ask for the model-specific manual or a bounded demonstration if a required function is unclear. “VPN supported” alone does not establish certificate handling, concurrent users, pass-through to a PLC discovery tool or a safe update process.
Use current model documentation and the site's own requirements for selection. For commissioning, keep the topology, addressing plan, access approvals, test results, configuration backup and rollback owner together so the next engineer can reproduce the path.
FAQ
Does a cellular router need a public IP for remote PLC access?
Not always. A router-initiated tunnel to a reachable VPN endpoint can work when the carrier uses private addressing or CGNAT. The endpoint, authentication, routes and firewall rules still need verification.
Can a VPN connection by itself make a PLC safe to access?
No. Limit each user to required devices and services, retain logs and apply the site's authorization process before changing programs or process settings. Separate read-only monitoring from control access.
Why can the VPN connect while the PLC tool cannot find the device?
The client may lack a route or return path, a firewall rule may block the engineering service, or the tool may depend on discovery broadcasts that do not traverse the routed tunnel. Test the device IP and vendor service explicitly.
How should repeated PLC subnets at customer sites be handled?
Document which site each address belongs to and use a site-specific NAT or renumbering plan inside the controlled access architecture. A shared 192.168.1.0/24 route cannot identify two different machines on its own.